Black Binder 2026 Upgraded Tool
Black Binder
Simple .NET File Binder
Features
Small Stub 15kb
Support Multiple Files
Screenshot
LEGAL DISCLAIMER PLEASE READ!
I, the creator and all those associated with the development and production of this program are not responsible for any actions and or damages caused by this software. You bear the full responsibility of your actions and acknowledge that this software was created for educational purposes only. This software's intended purpose is NOT to be used maliciously, or on any system that you do not have own or have explicit permission to operate and use this program on. By using this software, you automatically agree to the above.
License
This project is licensed under the MIT License
Babylon RAT
What kind of malware is Babylon?
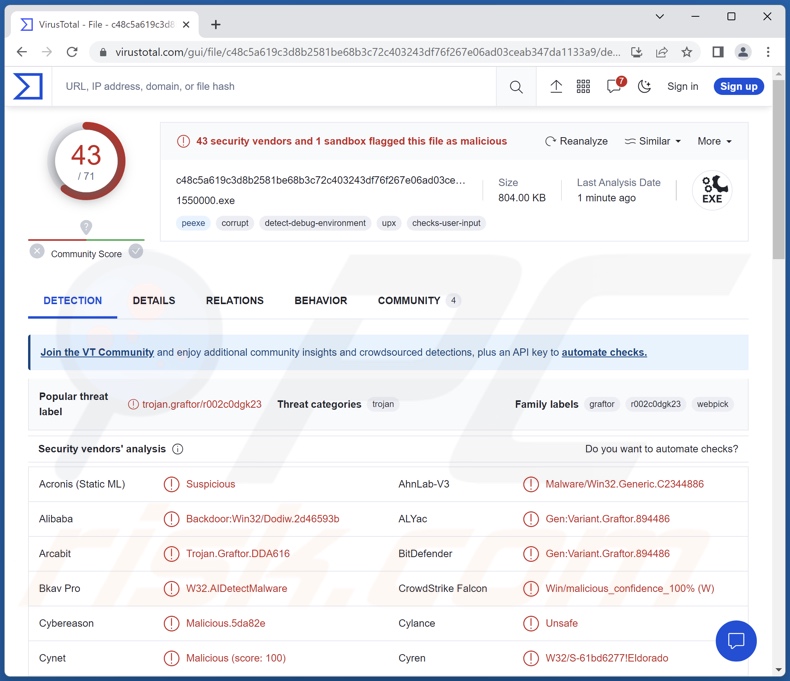
Babylon is the name of a Remote Access Trojan (RAT). This program is designed to allow remote access and control over infected machines. Like most trojans of this kind, Babylon is multi-functional. It can perform various commands on compromised devices, and as such, it is deemed to be a high-risk threat.
Babylon malware overview
The Babylon RAT enables remote access and control over infected machines. Following successful infiltration, this malware starts gathering relevant device data, e.g., hardware details, OS version and other system information, device name, username, IP address (geolocation), active window, and so on.
Babylon has anti-detection capabilities and can evade being detected by security tools. It can receive and execute various commands on compromised systems. Furthermore, this trojan can self-spread through the local network.
Babylon can also launch DDoS (Distributed Denial-of-Service) attacks. This activity relies on multiple sources (e.g., a botnet) to flood a target with requests – thus preventing legitimate ones from coming in, disrupting the service or even shutting it down. For example, DDoS attacks can be leveraged against a website or company – thus impeding or ceasing their operations.
Additionally, Babylon has information-stealing capabilities. This program can extract log-in credentials (i.e., usernames/passwords) from various installed applications, including browsers.
To summarize, the presence of software like Babylon on devices can lead to severe privacy issues, financial losses, and identity theft.
If you believe that your device is infected with the Babylon RAT (or other malware) – perform a full system scan using an anti-virus and remove all threats without delay.
2026 Crypter With Unlimited Taks
Xencrypt:
Bypasses AMSI and all modern AVs in use on VirusTotal (as of writing)
Compresses and encrypts powershell scripts
Has a minimal and often even negative (thanks to the compression) overhead
Randomizes variable names to further obfuscate the decrypter stub
Randomizes encryption, compression and even the order that the statements appear in the code for maximum entropy!
Super easy to modify to create your own crypter variant
Supports recursive layering (crypter crypting the crypted output), tested up to 500 layers.
Supports Import-Module as well as standard running as long as the input script also supported it
GPLv3 -- Free and open-source!
All features in a single file so you can take it with you anywhere!
Is despite all of the above not a silver bullet for every configuration -- caveat emptor!
0x0 Crypter - Free open sourced Crypter.
Overview
0x0 Crypter is a open sourced crypter fully coded by @MpCmdRun
? Features
? Base64 Protection - Provides a basic protection to your exe on runtime.
?️ AMSI Bypass - Provides a temporary Bypass to the AmsiScanBuffer on Windows 10 and 11.
?️ ETW Bypass - Provides a temporary ETW Bypass on Windows 10 and 11.
? Run as admin - Provides the applicaiton to be ran as administrator (RunAs UAC Bypass).
? Startup - Creates a scheduled Task to run this .exe everytime to computer turns back on.
[CRACK] Limitless Logger v5.7 & RAT
RAT stands for Remote Access Trojan. It is a type of malicious software that allows unauthorized individuals to remotely control a computer system. While RAT software can be used for legitimate purposes such as remote administration and tech support, it is often associated with cyber criminal activities.
Benefits of using RAT software include:
Remote administration: RAT software can enable system administrators to remotely manage and troubleshoot computer systems, which can be especially useful in large networks or when physical access to the system is not possible.
Tech support: RAT software can be utilized by tech support professionals to provide remote assistance and resolve technical issues for users.
Access: RAT software allows users to access and control a computer system from a remote location, providing flexibility and convenience.
However, it is important to note that RAT software can also be exploited by cybercriminals to gain unauthorized access to systems, steal sensitive information, or perform malicious activities.
Brutus AET 2 details
Description
Brutus is one of the most popular Bruteforce password cracker. It is used to find out HTTP, POP3, FTP and Telnet servers' passwords. It can simultaneously build 60 connections. One can extend this tool with plugins. Facilitate dictionary based user/password attacks against various network applications. from the doc: 'It is a remote interactive authentication agent. Brutus is used to recover valid access tokens (usually a username and password) for a given target system. Examples of a supported target system might be an FTP server, a password protected web page, a router console a POP3 server etc.'
Alias
Application/Brutus.A [Panda]
Exe
Father Of RATS The Collapse HVNC RATCollapse HVNC RATCollapse HVNC RAT is a type of Remote Access Trojan (RAT) associated with Hidden Virtual Network Computing (HVNC) technology. In cybersecurity discussions, HVNC malware is commonly analyzed because it allows attackers to operate a hidden desktop session on infected systems without the victim noticing visible activity.The term “HVNC” stands for Hidden Virtual Network Computing, a technique often abused by cybercriminals to remotely interact with compromised machines silently.Collapse HVNC RAT is generally discussed in malware research communities due to its stealth capabilities, persistence techniques, and remote-control functions.
Stich Python RAT is a term often used in cybersecurity discussions to describe a Python-based Remote Access Trojan (RAT) concept. Such threats are commonly referenced in threat intelligence, malware analysis, and defensive security research. Understanding how these threats operate at a high level is essential for developers, system administrators, and everyday users to protect digital environments.
This article is written only for educational and defensive purposes, helping readers understand risks, indicators, and prevention strategies without enabling misuse.
What Is Stich Python RAT?
Stich Python RAT refers to a remote access threat model implemented using the Python programming language. RATs are malicious programs designed to remotely control systems without user consent.
Python is sometimes referenced in malware research due to its cross-platform nature and ease of development, making awareness especially important.
Important: This article does not explain how such software is created or deployed.
Potential Risks Associated with RAT-Type Threats If a system is compromised by a RAT-style threat, it may face:
Unauthorized remote access
Data exposure or leakage
Monitoring of user activity
System manipulation
Long-term persistence risks
These risks highlight the importance of preventive cybersecurity practices.
SharpEye-RAT 1.0 Beta 2
SharpEye-RAT is analyzed as a remote access threat model in cybersecurity research.
Security Risks
Unauthorized system access
Surveillance risk
Data exposure
Defensive Insight
Use endpoint protection
Monitor remote connections