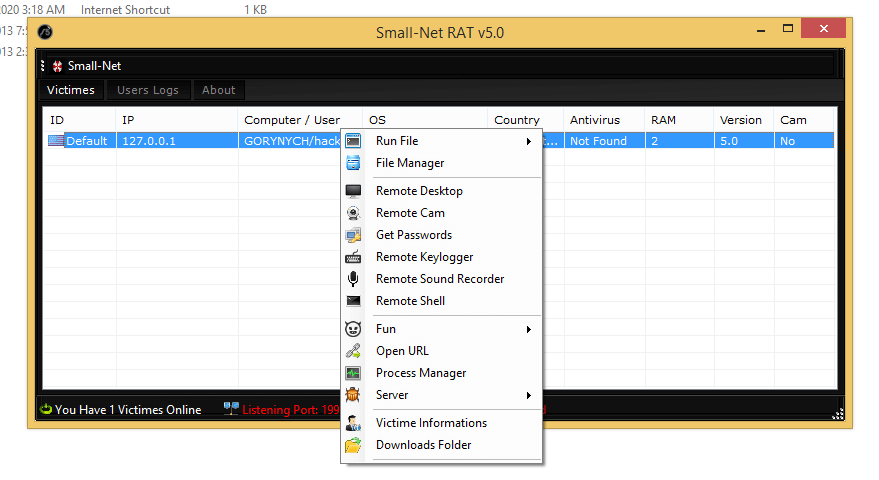
Small Net RAT v5.0 is a highly optimized remote administration tool that has been repurposed for unauthorized system access. The “Small Net” designation reflects both its modest file size (under 500KB) and its efficient use of network resources.
Features Overview
Process manager (running apps control karna)
Startup persistence (system restart ke baad bhi run hona)
Registry editor access (Windows settings modify karna)
Password stealing modules (browser & app credentials)
Remote command execution (CMD commands run karna)
Anti-detection / obfuscation techniques
Plugin system (extra malicious modules add karna)
DarkDDoSer 5.6C Cracked is promoted as a Distributed Denial-of-Service (DDoS)
stress-testing tool aimed at generating high-volume network traffic against
targeted systems or services. Tools in this category are frequently associated
with botnet activity, service disruption, and unauthorized network attacks,
although some are marketed for network stress testing and security research
As cyber threats continue to target critical infrastructure, Smad SSH Scanner 2024 stands out as a vital solution for IT security teams.
Features Overview
SSH server scanning via port 22 and 443
Login checking using username and password combos
IP range and bulk scanning support
LIVE / DIE SSH detection system
FRESH SSH identification (working internet access check)
Geo-location detection (country, state, city of SSH IP)
Blacklisted SSH server detection
Crypto Wallet Replacer 2024 is described as a clipboard-hijacking malware associated
with replacing copied cryptocurrency wallet addresses with attacker-controlled
addresses during transactions. Security researchers warn that clipboard
hijackers are commonly used in crypto theft campaigns targeting
wallet users and traders
Features
Clipboard wallet replacement
Crypto address monitoring
Background stealth execution
Multi-wallet targeting
Automatic address swapping
System persistence support
Remote configuration handling
Shell FINDER V-7 is likely a tool designed to scan servers or websites for accessible web shells or vulnerable endpoints. Web shells are scripts that allow remote access to web servers, so this tool is often used in ethical hacking, penetration testing, and security research to identify and secure compromised systems.
Highlights
Webshell Detection – Scans websites or servers for hidden webshells.
Vulnerability Scanning – Checks for insecure scripts or upload points that attackers might exploit.
Automated Scanning – Quickly scans multiple directories or URLs.
File Analysis – Examines suspicious files for backdoor behavior.
Reporting & Logging – Provides logs of detected shells or vulnerabilities.
Command Execution Simulation – Tests if detected shells allow remote commands (in controlled environments).
Introducing SMS Botnet 2026, an innovative cybersecurity tool engineered to build and control SMS-driven botnets for in-depth threat analysis and defensive training.
Features Overview
Multiple devices ko control karke SMS send/relay network banata hai.
Bulk SMS sending (large-scale messaging automation).
OTP / verification SMS flooding (harassment or abuse campaigns).
API-based SMS gateway abuse (telecom endpoints exploit).
Multi-region targeting (different countries/operators ko target karna).
Command-and-Control (C2) panel se remote control.
Sauron Locker 2026 is likely a ransomware-type tool designed to encrypt or lock user files or systems and demand a ransom for access restoration. The 2026 version implies it’s a modern or updated release, potentially with enhanced encryption methods or evasion techniques. Such tools are primarily studied in cybersecurity research and malware analysis labs to understand ransomware behavior and develop defenses.
Highlights
File Encryption / Locking – Encrypts files or locks access to certain directories or entire drives.
Ransom Note Generation – Displays instructions demanding payment to restore access.
Strong Encryption Algorithms – Uses modern encryption methods to make file recovery difficult without keys.
Stealth & Evasion – May attempt to bypass antivirus or security software.
Persistence Mechanisms – Ensures the ransomware runs on system reboot.
As email continues to serve as a critical communication channel for businesses and individuals alike, cybercriminals have developed increasingly sophisticated tools to exploit vulnerabilities in email infrastructure.
Features Overview
SMTP email accounts aur servers ko brute-force / login testing ke liye use hota hai.
Bulk email credentials checking (multiple accounts ek sath test karna).
SMTP authentication verify karta hai (valid/invalid login detect).
Username & password combo testing support karta hai.
Multi-threading scanning system use karta hai taake fast checking ho.
Proxy support (IP hide karne ke liye) use kiya jata hai.