GoDirSearch
Overview
godirsearch is a fast and modern Go-based web path scanner designed for efficient endpoint discovery on authorized targets. It combines concurrency, wildcard detection, adaptive rate control, recursive scanning, flexible filtering, proxy support, and multi-format reporting in a lightweight CLI.
Built for people who want a scanner that feels clean, fast, and practical without becoming bloated.
High-speed concurrent scanning
Supports single target, target list, and CIDR range
Wildcard-aware detection to reduce noisy false positives
Recursive mode with configurable depth and trigger statuses
Adaptive limiter that reacts to 429 and 503
HTTP/2, custom headers, cookies, request body, and custom methods
Rotating User-Agent support
Proxy and proxy-list rotation support
Smart wordlist expansion with extensions, prefixes, suffixes, blacklist, and backup patterns
Fine-grained filtering system for status, size, redirect, and body matching
Export to plain text, JSONL, CSV, HTML, and Markdown
Built-in progress stats and graceful shutdown
Grieve Crypter 2026
Inroduction
Grieve Crypter 2026(reflective) PE loader that enables in-memory execution of native PE files(EXE, DLL, SYS...). It enables stealthy in-memory payload deployment that can be used to bypass anti-virus, firewall, IDS, IPS products, and application white-listing mitigations. Reflective payloads generated by Amber can either be staged from a remote server or executed directly in memory much like a generic shellcode. By default, every generated payload is encoded using the new generation SGN encoder. Amber uses CRC32_API and IAT_API for inconspicuously resolving the Windows API function addresses. After the PE file is loaded and executed in memory, the reflective payload is erased for evading memory scanners.
Hijack This
HiJackThis+
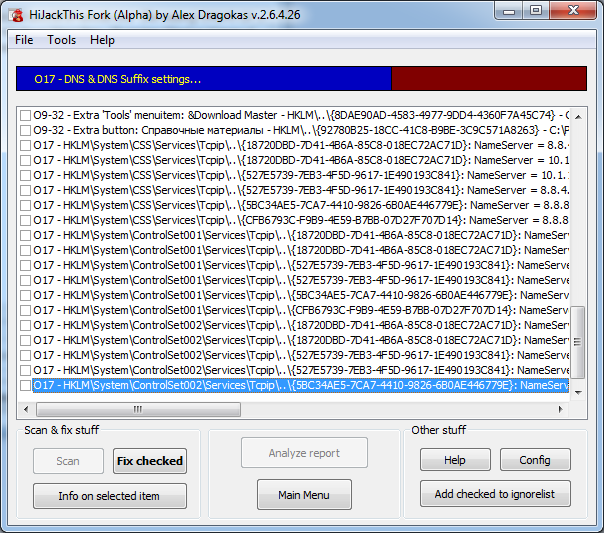
HiJackThis+ (Plus) (previously called: HiJackThis Fork v3) is a fork and a continuation of the original Trend Micro HiJackThis by Merijn Bellekom development, once a well-known tool.
At the moment, it is a step-by-step 100% rewritten source code of the original engine, aimed to provide a full compatiblity with the most recent Windows OS and a balance beetween compiling very fast results in logfile and combatting with the most popular malware, inluding the one not known to other antiviruses.
It is made by Alex Dragokas - a lawyer, security observer and malware researcher.
Overview
HiJackThis+ is a free utility for Microsoft Windows that scans your computer for settings changed by adware, spyware, malware and other unwanted programs. Shortly, consider it like Sysinternals Autoruns.
The difference from classical antiviruses is the ability to function without constant database updates, because HiJackThis+ primarily detects hijacking methods rather than comparing items against a pre-built database (signatures). This allows it to detect new or previously unknown malware - but it also makes no distinction between safe and unsafe items. Users are expected to research all scanned items manually, and only remove items from their PC when absolutely appropriate.
Therefore, FALSE POSITIVES ARE LIKELY. If you are ever unsure, you should consult with a knowledgeable expert BEFORE deleting anything.
HiJackThis+ is not a replacement of a classical antivirus. It doesn't provide a real-time protection, because it is a passive scanner only. Consider it as an addition. However, you can use it in form of boot-up automatical scanner in the following way:
Run the scanning by clicking "Do a system scan only"
Add all items in the ignore-list
Set up boot-up scan in menu "File" - "Settings" - "Add HiJackThis to startup"
Next time when user logged in, HiJackThis will silently scan your OS and display UI if only new records in your system were found.
Tutorial
Please, refer to the List of tutorials
Features
Lists non-default settings in the registry, hard drive and memory related to autostart
Generates organized, easily readable reports
Does not use a database of specific malware, adware, etc
Detects potential methods used by hijackers
Can be configured to automatically scan at system boot up
Advantages
Short logs
Fast scans
Not necessarily to create fixing scripts manually
No need for internet access or recurring database updates
Already familiar to many people
Portable
New in version 2.6+
Detects several new hijacking methods
Fully supports new versions of OS Windows
New and updated supplementary tools
Improved interface, security and backups
HiJackThis+ also comes with several modules useful for specific analysis and removing malware from a computer:
StartupList 2 (*new*)
Process Manager
Uninstall Manager
Hosts File Manager
Alternative Data Spy
Services Removing Tool
Batch Digital Signature Checker (*new*)
Registry Key Type Analyzer (*new*)
Registry Key Unlocker (*new*)
Files DACL Unlocker (*new*)
Check Browsers' LNK & ClearLNK (as downloadable components) (*new*)
Hoic 1.1
DDoS attack using HOIC
A distribute denial of services (DDoS) attack involves a group of compromised systems usually infected with Trojans used to perform a DoS attack on a target system or network.
Objectives
Perform DDoS attack - HTTP flooding
Requisites
Kali Linux virtual machine (Target)
Windows Server, Windows 10 and Windows 7 virtual machine (Attackers)
Overview of HOIC
High Orbit Ion Cannon (HOIC) is a free, open-source network stress application developed by Anonymous, a hacktivist collective, to replace the Low Orbit Ion Cannon (LOIC). Used for denial of service (DoS) and distributed denial of service (DDoS) attacks, it functions by flooding target systems with junk HTTP GET and POST requests.
Log in to Virtual Machines
Before beginning this lab, turn on and log in to all virtual machines on this lab (Windows 7, 10, Server and Kali Linux).
Copy the High Orbit Ion Cannon (HOIC) folder onto all the Windows virtual machines(3).
Configure HOIC
Switch to the Windows 10 and open the HOIC (hoic2.1.exe)
On the HOIC GUI, click '+' to add the target.
ABCProxy.com 2026 is a premium proxy service that offers residential, ISP, and datacenter proxies for secure and reliable internet access.
Key Features
[*]Large global residential IP pool
[*]Residential, ISP, and datacenter proxies
[*]HTTP, HTTPS, and SOCKS5 support
[*]Rotating and static IP options
[*]190+ country coverage.
*~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~*
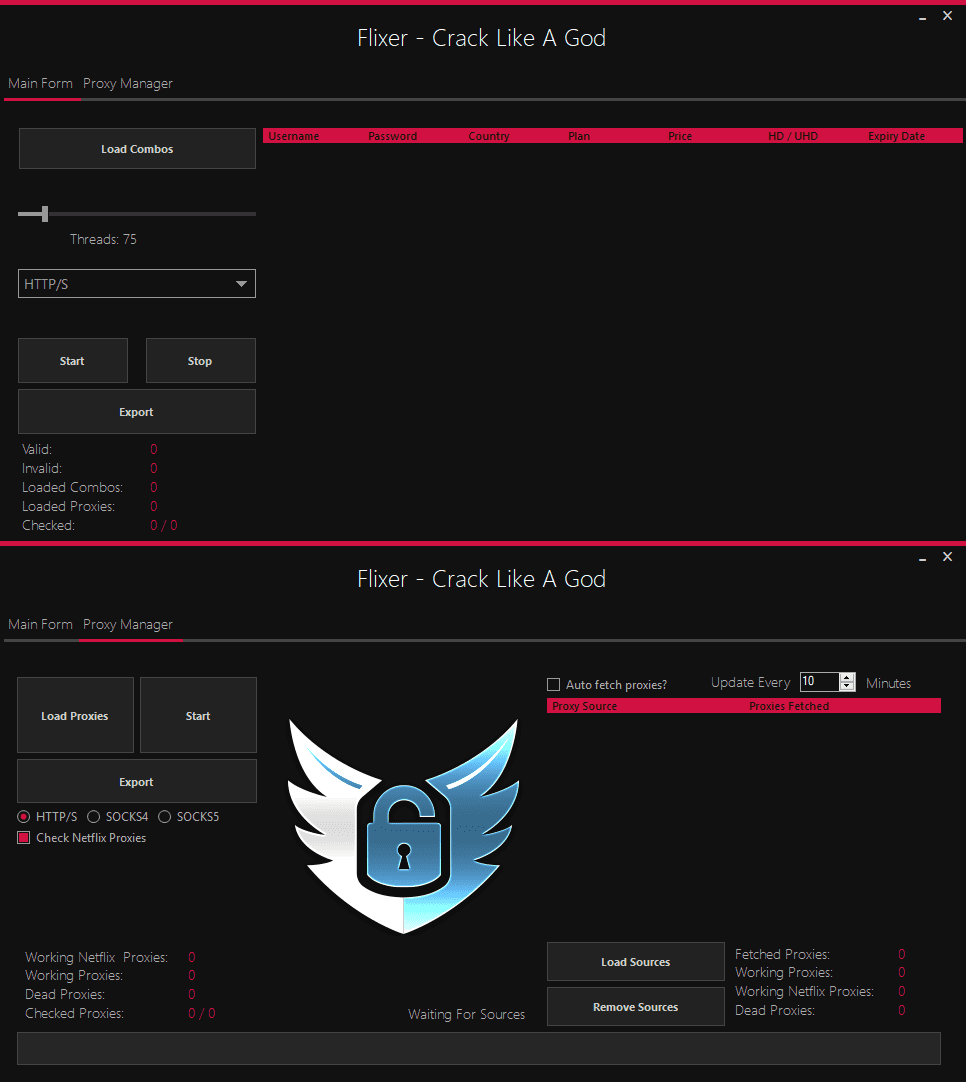
[+] Customizable Threads Numbers Up to 700 Threads!
[+] Supports All the proxies Types! HTTP, SOCKS4, SOCKS5
[+] A full integrated customizable Proxies Scrapper-Grabber
[+] A dedicated Proxies Checker Linked with Netflix API
[+] Full Capture of The Accounts Details (Plan, Price, Expire Date, Country, HD/UHD)
*~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~*
You can create thousands of Blockchain Wallet accounts and pick out the good ones for a hefty profit. Or you can also make thousands of accounts for a bomber bot. Supports proxies.
Advance Keylogger & Stealer
Introduction: Keylogger Malware
Cybereason’s Nocturnus team is tracking a new keylogger gaining traction among cybercriminals called Phoenix. The keylogger first emerged in July 2019 packed with a myriad of information-stealing features. These features extend beyond solely logging keystrokes, to the point where we are inclined to classify it as an infostealer.
This research explains several aspects of the Phoenix keylogger, including:
A Look Into the Underground Community: The underground, ongoing marketing efforts to promote Phoenix and its reception in the underground community.
A Technical Breakdown: A technical breakdown of the Phoenix keylogger, including info stealing capabilities, communication through Telegram, and potential persistence.
The Connection to a Previous Keylogger: The discovery of the Phoenix keylogger’s connection to the “orphaned” Alpha keylogger.
Key Findings
The Phoenix Keylogger: The Cybereason Nocturnus team is investigating multiple incidents of a new, emerging keylogger called Phoenix, and is now able to provide details into the keylogger’s operations and its creator.
Steals Data From Multiple Sources: Phoenix operates under a malware-as-a-service model and steals personal data from almost 20 different browsers, four different mail clients, FTP clients, and chat clients.
Tries to Stop over 80 Security Products: On top of its information stealing features, Phoenix has several defensive and evasive mechanisms to avoid analysis and detection, including an Anti-AV module that tries to kill the processes of over 80 different security products and analysis tools.
Targets Across Continents: Despite Phoenix having been released in July 2019, it has already targeted victims across North America, the United Kingdom, France, Germany and other parts of Europe and the Middle East. We expect more regions to be affected as it gains popularity.
Exfiltrates Data through Telegram: Phoenix offers common SMTP and FTP exfiltration protocols, but also supports data exfiltration over Telegram. Telegram, a popular chat application worldwide, is leveraged by cybercriminals for its legitimacy and end-to-end encryption.
Has the Same Author as the Alpha Keylogger: Phoenix was clearly authored by the same team behind the Alpha keylogger, which disappeared earlier this year.
“Malware for the People”: This research showcases the ever-growing popularity of the Malware-as-a-Service model in the cybercrime ecosystem. Malware authors are developing malware that is easy for any user to operate and comes bundled with customer support