Latest Threads


High-performance Crypto Clippers Software | Source Code


General Hacking    1 Replies

botty, 06-26-2026, 09:21 PM

High-performance Crypto Clippers Software  | Source Code
This article is purely educational and focuses on awareness, detection, and prevention, helping users, developers, and businesses understand the risks and protect themselves.
 Why Is C++ Often Mentioned With Crypto Clippers?
C++ is a powerful programming language commonly used for:
System-level applications
High-performance software
Operating system utilities
Because of these capabilities, malware researchers often analyze C++-based threats to understand how attackers exploit low-level system access.
 Important: Discussing C++ here is for defensive cybersecurity awareness, not development of malicious software.
[Image: shutterstock_148972376.jpg?1427488734]
[/center]
[/center]


  Open Thread

Liberium 2.1 stealth mechanisms Stealer Tool


Hacking Tools    No Replies

botty, 06-25-2026, 07:59 PM

Liberium 2.1
Liberium 2.1
The world of cybersecurity continues to evolve rapidly, and with this growth comes increasingly sophisticated threats. One topic gaining attention in underground cybersecurity discussions is Liberium RAT 2.1. Remote Administration Tools, commonly known as RATs, are applications designed to remotely control systems over a network connection. While some RATs are created for legitimate administrative purposes, others are associated with malicious cyber activities.
Liberium RAT 2.1 has become notable because of its advanced capabilities, stealth mechanisms, and remote management features. Cybersecurity researchers, ethical hackers, and digital security professionals frequently analyze such tools to understand attack methods and improve defensive strategies.
This article provides a detailed overview of Liberium RAT 2.1, its features, risks, technical behavior, cybersecurity implications, and methods organizations can use to protect their systems.
[Image: Liberium3.webp]

[/center]
[/center]


  Open Thread

Liberium 2.1 stealth mechanisms Stealer Tool


Hacking Tools    No Replies

botty, 06-25-2026, 07:58 PM

Predator 1.6
Predator 1.6
Introduction
Table of Contents
Predator 1.6 is referenced as a remote surveillance-style malware, emphasizing the need for strict access control and monitoring.
Key Security Concerns
Unauthorized remote access
System manipulation
Persistent backdoor risks
Prevention Best Practices
[Image: Predator.webp]

[/center]
[/center]


  Open Thread

Shadow Batch Virus Gen Disable unknown scripts


Hacking Tools    No Replies

botty, 06-25-2026, 07:57 PM

Shadow Batch Virus Gen
Shadow Batch Virus Gen tool is associated with batch script-based malware behavior analysis.
Shadow Batch Virus Security Risks
Script automation misuse
System command abuse
Execution-based threats
Defensive Insight
Disable unknown scripts
Use execution policies
Monitor system processes
[Image: Inshadow.webp]

[/center]


  Open Thread

ABCProxy.CoM Brute And Latest Version Checker 2026


Checker Tool    No Replies

botty, 06-24-2026, 05:35 PM

[Image: images?q=tbn:ANd9GcR-qDh5GOYx5BKdHpqfsoA...B2hJxnhQ&s]
ABCProxy.CoM Brute And Latest Version Checker 2026
is a free HTTP-based account testing tool with SOCKS5/HTTP proxy support, CAPTCHA bypass, and NodeJS ...

[/center]
[/center]


  Open Thread

BSC & ETH Crypto Sniper Bot 2026


General Hacking    No Replies

botty, 06-24-2026, 05:34 PM

[Image: d139ea70-f1b7-4703-ae25-8c8e379014ee]

BSC & ETH Crypto Sniper Bot 2026

BSC & ETH Crypto Sniper Bot 2026
Welcome to BSC-AutoCryptoTrade, the ultimate automated trading bot for the Binance Smart Chain (BSC) network! This powerful bot scans all tokens on the BSC network and executes trades based on sophisticated algorithms.
Buy Target: Automatically buys tokens when they hit a specified target. Sell Target: Sells tokens at the optimal price point.
StopLoss Target: Minimizes losses by selling tokens when they drop to a certain price.
Minimum Volume 24hours: Ensures liquidity by trading tokens with sufficient volume.
Minimum Buy: Sets a floor for the smallest trade amount.
Maximum Buy: Caps the largest trade amount to manage risk.
The bot can compare data based on the last fetched data (TimeFrame Mode) or the last event (Event Mode). You can customize the timeframe for comparisons, making this bot incredibly flexible to suit your trading strategy!
Proven Success\
I have personally used this bot to turn 8K USD into 6 Figures in just 3 months!
Clone the repository:
git clone
cd BSC-AutoCryptoTrade
Install the requirements:
pip install -r requirements.txt
Configure the environment variables:
Copy the .env.example to .env and fill in the required values:
cp app_dir/.env.example app_dir/.env
Run the bot:
python app.py
Add Wallet:
Follow the instructions in the bot interface to add your wallet.
Configure the wallet:
Click open configuration on wallet that you want to configure
Fund the wallet:
Transfer the required amount of BNB or other tokens to your configured wallet address.
Run the bot:


[/center]


[/center]


  Open Thread

Backdoor access concepts SubSeven 2.2


Checker Tool    No Replies

botty, 06-24-2026, 05:32 PM

SubSeven 2.2

SubSeven 2.2
Overview
Table of Contents
SubSeven 2.2 is a historic RAT used to study early remote access threats.
Security Risks
Backdoor access concepts
System control risks
Defensive Insight
Important for historical malware study
Helps understand modern RAT evolution
[Image: Sub7.webp]


[/center]


[/center]


  Open Thread

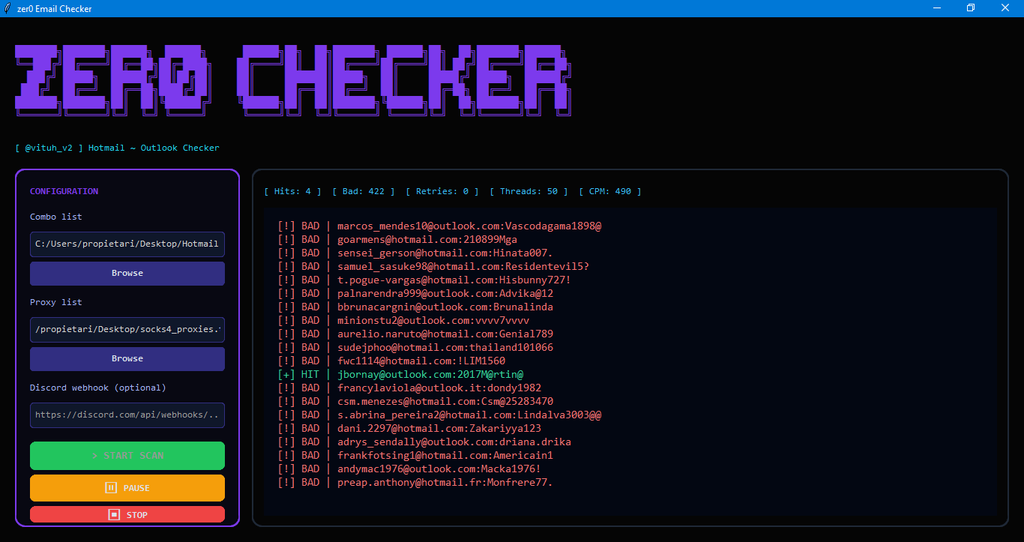
Zer0 Checker - HotmailOutlook Checker


Checker Tool    No Replies

pking25, 06-23-2026, 10:37 AM

[Image: bdwC3.png]
Zer0 Checker - HotmailOutlook Checker

Arhive password 123

|
|


  Open Thread

HardCore Soft 0.0.1 Helps identify unknown threats


Checker Tool    No Replies

botty, 06-22-2026, 03:09 PM

HardCore Soft 0.0.1

HardCore Soft 0.0.1
HardCore Soft 0.0.1 is often discussed as an experimental software sample used in reverse engineering analysis.
Security Risks
Unstable execution behavior
Unknown functionality
Possible malicious patterns
Defensive Insight
Useful for malware researchers
Helps identify unknown threats
Improves sandbox analysis techniques
[Image: HC2.webp]


[/center]


[/center]


  Open Thread

Netflix Checker 2026 commonly known as credential stuffing


Checker Tool    No Replies

botty, 06-21-2026, 03:18 PM

[Image: netflix-checker-2-1024x443.webp]

[center]Netflix Checker 2026 [center]
[center]

[B][center]

The phrase Netflix Checker 2025 generally refers to tools or scripts that attempt to verify login credentials against Netflix accounts.

? Key Idea:
These tools test combinations of emails and passwords
Often rely on leaked or reused credentials
Used in unauthorized ways on compromised data
? This process is commonly known as credential stuffing

[center]
[B][center]

[center]
[center]
[center]
[center]

[center]
[center]


  Open Thread