Cooked Grabber 2026 is described in cybersecurity contexts as an information-stealing malware designed to collect sensitive data from infected systems. It typically targets stored credentials, browser data, and other personal information, then transfers it to remote command-and-control (C2) servers. Such tools are analyzed in cybersecurity research to understand modern data theft and credential harvesting techniques.
Key aspect
Browser credential and password extraction
Cookie and session token theft (account takeover risk)
Cryptocurrency wallet data collection
System information gathering (OS, hardware, IP details)
File scanning for sensitive documents and stored credentials
Data exfiltration to remote C2 servers
COSMO Stealer 2026 is described in cybersecurity contexts as an information-stealing malware designed to collect sensitive user data from infected systems. Such malware families typically target browser credentials, cookies, cryptocurrency wallets, and other personal information, sending the stolen data to remote command-and-control (C2) servers.
Key aspect
Browser password and credential theft
Extraction of cookies and session tokens
Cryptocurrency wallet data harvesting
System information collection (OS, hardware, IP data)
File scanning for sensitive documents or stored credentials
Data exfiltration to remote command-and-control servers
Introducing LuxNet RAT Cracked 2026, a sophisticated remote access tool engineered for ethical hackers and security experts to probe and fortify digital defenses. It serves to replicate real-world cyber threats, helping organizations identify weaknesses before adversaries exploit them. Unlike standard versions, this cracked iteration delivers unrestricted features, empowering users with unparalleled investigative capabilities.
Features Overview
Invisible Operation: Runs silently in the background, evading antivirus detection for authentic threat simulation.
Cross-OS Compatibility: Works seamlessly on Windows, macOS, Linux, and even mobile devices, expanding testing reach.
Comprehensive Monitoring: Tracks user actions, system processes, and file transfers in real time for detailed security audits.
Modular Plugins: Allows integration of custom plugins to enhance functionality, such as webcam access or data exfiltration.
cPanel Checker Account 2026 is described in cybersecurity contexts as a utility associated with testing and validating access to cPanel-based hosting accounts. Such tools are often referenced in discussions about hosting security, credential auditing, and detection of weak authentication practices. Security researchers study these behaviors to improve account protection and prevent unauthorized access attempts against web hosting platforms.
Key aspect
Validation of cPanel account accessibility and login responses
Detection of weak or misconfigured authentication settings
Automated checking of multiple hosting accounts or domains
Multi-threaded processing for rapid account verification
Logging and filtering of tested account results
Proxy/IP rotation support for network requests
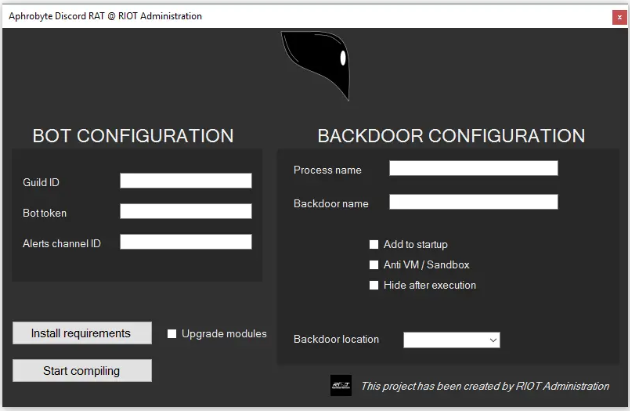
Aphrobyte RAT 2026 is described in cybersecurity contexts as a Remote Access Trojan used to gain unauthorized control over infected systems. It typically operates through a command-and-control (C2) infrastructure, allowing attackers to monitor activity, access files, and execute commands remotely. Such malware families are analyzed in cybersecurity research for their role in system compromise and data theft.
Key aspect
Remote system access via command-and-control (C2) server
File management (upload, download, delete operations)
Keylogging for capturing user input and credentials
Screen monitoring and activity tracking
Remote command execution on infected machines
Persistence mechanisms (startup/boot auto-run)
“Ultimate Account Checker” tools are typically presented as automation software used to test large lists of
usernames and passwords against online services. They are often distributed through unofficial sites and
are associated with credential validation processes that may involve unauthorized or abusive login attempts.
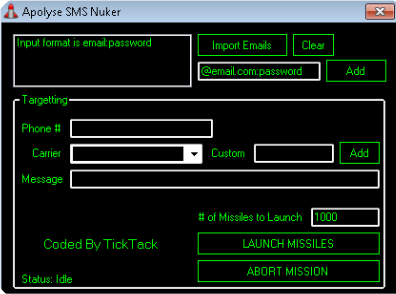
Apolyse SMS Nuker 2026 is described in cybersecurity contexts as a type of abusive messaging tool designed to generate a large volume of SMS messages toward a target phone number. Tools like this are associated with SMS flooding or message spam attacks, which can disrupt mobile services and are considered a form of digital harassment.
Key aspect
High-volume automated SMS sending behavior
Target-based message flooding (single number or list)
Use of multiple gateways or APIs for message delivery
Rapid message repetition in short time intervals
Potential use of spoofed sender identities
Overload of mobile inbox / service disruption
Link Exploit 2024 represents a new and highly sophisticated evolution in the realm of hyperlink-based cyber threats, marking a significant leap from traditional phishing campaigns. Unlike classic attacks that rely solely on deceiving users into entering credentials on fake websites, this new breed of exploit combines advanced social engineering tactics
Arsium Ransomware Builder 2026 is described in cybersecurity contexts as a malicious ransomware-building toolkit that allows attackers to generate customized file-encrypting malware. It is used to create ransomware variants capable of locking victim files and demanding payment for decryption
Key aspect
Generates custom ransomware executables using a builder interface
File encryption using strong cryptographic algorithms (symmetrical/asymmetrical)
Adds unique file extensions after encryption (e.g., locked files)
Creates ransom notes with payment instructions
Offline or local execution capability (no server dependency in some variants)
Customizable attack settings (file types, directories, extensions)
The Layer 4 DDOS is continually challenged by an ever-evolving array of threats, with Distributed Denial of Service (DDoS) attacks remaining among the most persistent and disruptive. As attackers refine their techniques and leverage more sophisticated tools, defenders face increasing difficulty in protecting network infrastructures from large-scale, coordinated assaults designed to overwhelm resources and disrupt services.
Features Overview
Packet crafting (Scapy integration).
Proxy chaining (TOR/SOCKS5 support).
Dynamic spoofing (Randomized source IPs).
AI-driven attack patterns (Adapts to defenses).
Lightweight program for video/audio processing
Simple interface with minimal controls