Jshop.cc, bbmarket invitation/invite code, non VBV CC, CVV, Ransomware As a Service, funding bank accounts and credit cards, The New Genesis.Market Marketplace 2026, Web Shells, browser stealer, RAT, Payload, Botnet, Keylogger, non-VBV CC stores, list of Cardable Gateway 2D sites, virus, malware, Trojans. OTP/2FA bypass tool, Office 365 corporate logs, payroll, BEC, professional email compromise account shops, bank log sites, hacking and spamming account shops, brute force, cracking, tutorials, methods, guide, valid and legitimate onion sites, online banking and shop services, shell, dumps with PIN, fullz CC, bank open ups, deposit, pickups, magbo cc invitation code and cracking. You can also request for a particular country's CC/CVV shop you are looking for, and I will get it for you. Dumps with pin, real physical ID cards for UK, Canada, USA, and Australia to be delivered to your house, and fullz info are also available. I'm also a carder and spammer too, and you can also spread my ransomware file online and social media to earn good money from. An Example: -
Screenshots:
Video:
Readily available. You can contact me for more proves. Escrow is also accepted.
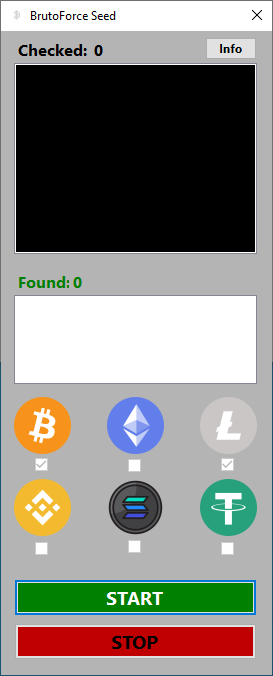
BrutoForce Seed v12.6.8 - Advanced Crypto Brute Forcing Tool
Discover the power of BrutoForce Seed v12.6.8, the ultimate brute forcing tool designed to unlock the secrets of popular cryptocurrencies. This advanced software leverages cutting-edge algorithms to check and recover lost or forgotten cryptocurrency seeds, making it an invaluable asset for digital currency enthusiasts and security professionals.
**Key Features:**
* **Multi-Crypto Support:** BrutoForce Seed v12.6.8 supports a wide range of cryptocurrencies including Bitcoin (BTC), Ethereum (ETH), Litecoin (LTC), Binance Coin (BNB), Solana (SOL), and Tether (USDT).
* **High-Speed Processing:** Experience lightning-fast seed checking and recovery with our optimized brute forcing engine.
* **User-Friendly Interface:** The intuitive design ensures ease of use, allowing both beginners and experts to efficiently navigate and operate the tool.
* **Real-Time Results:** Get instant feedback on checked and found seeds, displayed clearly in the results window.
* **Secure and Reliable:** Your data security is our priority. BrutoForce Seed ensures all operations are conducted safely, without compromising the integrity of your information.
Skuld Stealer 2026 modern information-stealing malware written in Golang
Skuld Stealer 2026 modern information-stealing malware written in Golang
What is Skuld Stealer 2026?
Skuld Stealer 2026 is a modern information-stealing malware written in Golang that focuses on extracting sensitive data from compromised Windows systems. The malware primarily targets Discord tokens, browser credentials, cookies, cryptocurrency wallets, and system information.
The project has attracted attention in the cybersecurity community because its source code is publicly available, allowing attackers to customize and deploy the malware in different cyber campaigns.Computer Security
Since Skuld Stealer 2026 is developed using Go (Golang), the compiled binaries are usually large and harder to analyze. This characteristic can help attackers evade certain security detection techniques.
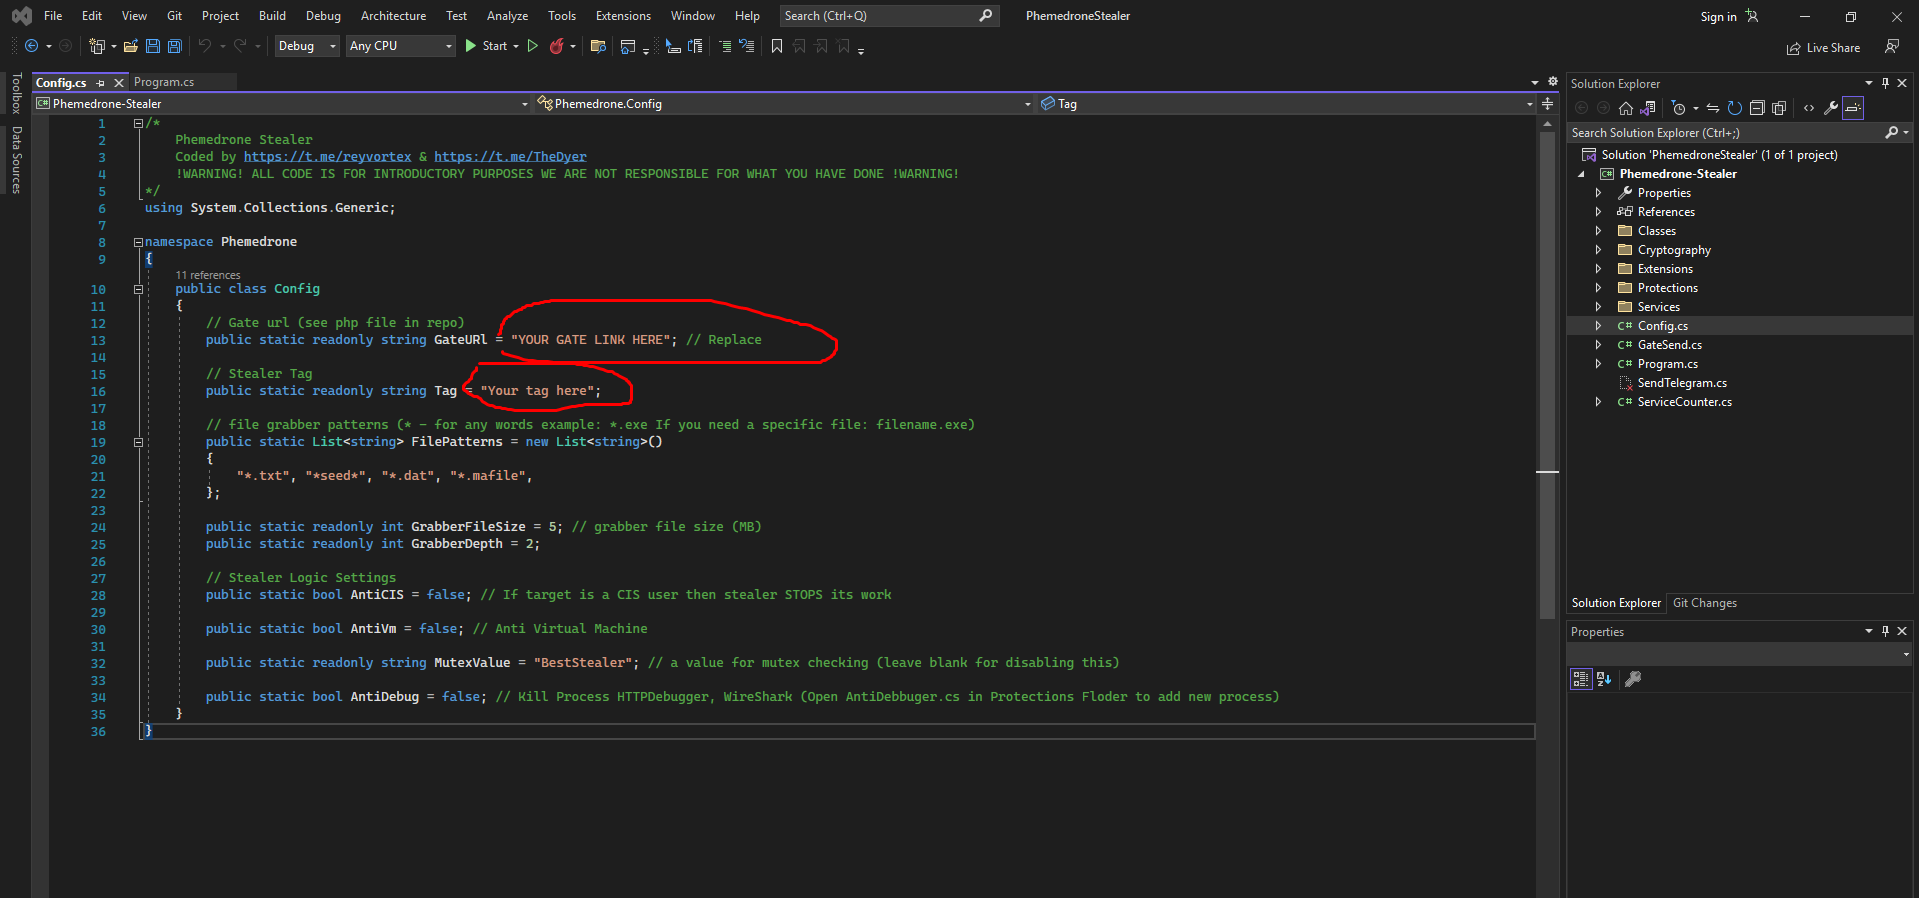
Phemedrone Stealer 2026
Phemedrone Stealer 2026 – Complete Malware Analysis, Features, Architecture & Cybersecurity Risks
Introduction to Phemedrone Stealer 2026
In recent years, information-stealing malware (infostealers) has become one of the most common threats in the cybersecurity landscape. These malware families are specifically designed to extract valuable digital data from infected systems and transmit it to remote servers controlled by attackers.Malware removal services
Phemedrone Stealer 2026 is one such advanced infostealer that has gained attention due to its lightweight architecture, memory-based data collection, and wide data-harvesting capabilities.
Developed in C#, this malware operates without external dependencies and uses an HTTP-based log system to send stolen information. Its design allows attackers to collect sensitive data such as:
• Browser credentials
• Cookies and session tokens
• Credit card data
• Messaging platform sessions
• Cryptocurrency wallet information
• Sensitive files stored on the system
Understanding how Phemedrone Stealer 2026 works is important for security researchers, malware analysts, and cybersecurity professionals who aim to detect, analyze, and prevent such threats.
Educational Disclaimer
This article is provided strictly for cybersecurity education, research, and awareness purposes.
The information discussed here helps analysts and defenders understand how infostealer malware operates so they can improve security defenses.Computer Security
Any misuse of this information for illegal activities is not supported and remains the responsibility of the individual involved.
What is Phemedrone Stealer 2026?
Phemedrone Stealer 2026 is a data-harvesting malware designed to extract confidential information from Windows systems.
Unlike many malware families that require multiple libraries or external dependencies, this stealer is designed to be simple, compact, and efficient.
Key characteristics
Written entirely in C#
No external libraries required
Lightweight executable file
Data collection performed directly in memory
Logs transmitted through HTTP
These features allow the malware to remain compact and easier to deploy across different systems.
Architecture of Phemedrone Stealer
The malware operates using a two-component architecture.
Stealer Stub
The stealer stub is the executable component that runs on the infected machine.
CoinMerce 2026 Cracked Tool – Complete Security Analysis
The rapid expansion of the cryptocurrency market has created new opportunities for traders and investors worldwide. However, the increasing popularity of digital assets has also attracted cybercriminal activities targeting cryptocurrency platforms.Brokerages & Day Trading
What Is CoinMerce 2026 Cracked?
Overview of the CoinMerce Checker Tool
CoinMerce 2026 Cracked is described as an automated credential checking application used to test massive databases of leaked usernames and passwords.Cybersecurity framework integration
These tools are commonly associated with credential stuffing attacks, where attackers attempt to log in using previously leaked credentials from data breaches.
Key Characteristics
Automated credential testing system
Supports large combo lists of email and password data
Identifies accounts with weak security protection
Organizes results for further analysis
Because many users reuse passwords across platforms, such tools attempt to exploit this behavior.
Hacking Android 2026
Hacking Android 2026
very useful book for starting hacker with full tools and tutorials
Chapter 1:Setting up the Lab
Chapter 2: Android Rooting
Chapter 3:Fundamental Building Blocks of android apps
Chapter 4:Overview of Attacking Android Apps
Chapter 5ata Storage And its Security
Chapter 6:Server Side Attacks
Chapter 7:Client Side Attack Static Analysis Techniques
Chapter 8:Client Side Attack Dynamic Analysis Techniques
Chapter 9:Android Malware
Chapter 10:Attacks on Android Devices
nordvpn-linuxNORDVPN PREMIUM ACCS TILL 2029 |WITH DEDICATED IP | NORDVPN | NORDVPN
nordvpn-linux
nordvpn-linux
NORDVPN PREMIUM ACCS TILL 2029 |WITH DEDICATED IP | NORDVPN
The NordVPN Linux application provides a simple and user-friendly command line interface for accessing all the different features of NordVPN. Users can choose from a list of server locations around the world, or let the application automatically select the best server for them. They can also customize their connection settings, such as choosing a specific protocol or enabling the kill switch feature.
The application manages:
network interfaces with the help of tuntap kernel interface,
firewall with the help of iptables,
routing with the help of iproute2 and
DNS with the help of systemd-resolved.
Versioning
The project follows
. Version tags and release branches must be named accordingly.
Contributing
We are happy to accept contributions for the project. Please check out Contribute.md file for more details on how to do so.
Building
You can find everything related to building, testing and environment setup in BUILD.md.
Installing
For installing an already released version please follow the instructions on our official page.
Solana-Drainer-Tool
SOL Drainer
Solana Network Security Research Tool
Educational • Isolated • Analytical • Secure
Research Overview
SOL Drainer is a specialized educational utility designed for security research and vulnerability assessment on the Solana network, assisting developers in understanding wallet security mechanisms.
Core Research Features Security Analysis
Wallet Vulnerability Testing: Educational assessment only
Transaction Security Research: Smart contract analysis
Network Threat Identification: Theoretical vulnerability study
Risk Evaluation: Academic security reporting
Safety Protocols
Complete testnet isolation
No mainnet connectivity
Educational simulation mode
Detailed research documentation
Critical Legal Notice
STRICT WARNING: This tool is provided EXCLUSIVELY FOR ACADEMIC RESEARCH AND EDUCATIONAL PURPOSES. Any use outside isolated testnet environments with test tokens is strictly prohibited. Users must adhere to all applicable laws and ethical guidelines. Never use on mainnet or with real assets.
VPN-Speed-Comparison-Tool
VPN Speed Comparison Tool
This is a tool, written in Python, for assessing network speed over VPN connections.
It is composed of two main parts: the daemon, which is invoked using the vpnspeedd command, and the client, which is invoked using the vpnspeed command. The daemon awaits instructions from the client and executes the given tests in the background. The client controls the test configuration and daemon life-cycle.
Detailed whitepaper with the methodology can be found here:
Dependencies:
apt-transport-https
ca-certificates
curl
docker-ce
docker-compose
git
gnupg
jq
python3-dev
python3-pip
python3-setuptools
python3-wheel
python3-yaml
software-properties-common
wireguard
Notes:
Test can be started by running scripts/setup.sh, which will install all dependencies.
This project was build and mainly tested using debian 10, other distribution of debian can be incompatible.
IP geolocation
For test execution ip geoservice is needed. In this project ipapi.co was selected.
Usage
First, clone the repository with the following command:
$ git clone
After cloning the repository and before starting the testing process, edit the configuration file to add VPN provider credentials and further customize test execution.
$ vi vpnspeed.yaml
Run using scripts/setup.sh
$ sudo ./scripts/setup.sh
Note:
Adding --dry-run to setup.sh will only install, but not start test with configuration.
$ sudo scripts/setup.sh --dry-run`
Local - manually
To run the tests locally, run the following commands in the project root. The following commands will start a docker container, start the vpnspeedd daemon on it and leave it running in the background:



 ata Storage And its Security