Spam_Mail_Prediction_using_Machine_Learning
Spam Mail Prediction Web App
This repository contains a web application that predicts whether an email is spam or not using a Logistic Regression model. The application is built with a user-friendly interface and offers real-time predictions based on the email content.
Overview
pam emails are a major issue in digital communication, causing various problems ranging from minor annoyances to severe security threats. This project aims to develop a solution to detect spam emails effectively using machine learning techniques. The application preprocesses email text using TF-IDF vectorization and classifies it with a Logistic Regression model.
Dataset
The dataset used for training the model consists of a collection of emails labeled as spam or not spam. The data has been preprocessed to remove noise and irrelevant information.
Results
The model achieves high accuracy in predicting spam emails, with key metrics as follows:
Accuracy: 96.59% These results demonstrate the model's effectiveness in distinguishing between spam and non-spam emails.
Conclusion
This project successfully demonstrates the use of machine learning for spam email detection. The Logistic Regression model, combined with TF-IDF vectorization, provides a reliable solution for predicting spam emails. Future improvements could include testing with larger datasets, experimenting with different models, and enhancing the web application's features.
Contributing
Contributions are welcome! If you have any suggestions or improvements, please create a pull request or open an issue.
ROBLOX ACCOUNT CHECKER CAPTURE
roblox-username-checker
Multi-threaded Roblox Username Checker using the official Roblox API. Handles rate-limits and etc. Don't leech, feel free to fork.
This program will create a folder named "valids" and automatically append/create text-files for each amount of characters.
Feel free to improve it and use this code as a base. Although credit for any project wether open-source or closed-source would be appreciated. It's really nothing special. It's just a web request spammer made by someone with no python knowledge.
How to run
1. Download/Clone repository
2. Extract/Open
3. Open cmd/powershell/terminal
4. pip install -r requirements.txt
4. Run: python main.py
VPN-Speed-Comparison-Tool
VPN Speed Comparison Tool
This is a tool, written in Python, for assessing network speed over VPN connections.
It is composed of two main parts: the daemon, which is invoked using the vpnspeedd command, and the client, which is invoked using the vpnspeed command. The daemon awaits instructions from the client and executes the given tests in the background. The client controls the test configuration and daemon life-cycle.
Detailed whitepaper with the methodology can be found here:
Dependencies:
apt-transport-https
ca-certificates
curl
docker-ce
docker-compose
git
gnupg
jq
python3-dev
python3-pip
python3-setuptools
python3-wheel
python3-yaml
software-properties-common
wireguard
Notes:
Test can be started by running scripts/setup.sh, which will install all dependencies.
This project was build and mainly tested using debian 10, other distribution of debian can be incompatible.
IP geolocation
For test execution ip geoservice is needed. In this project ipapi.co was selected.
Usage
First, clone the repository with the following command:
$ git clone
After cloning the repository and before starting the testing process, edit the configuration file to add VPN provider credentials and further customize test execution.
$ vi vpnspeed.yaml
Run using scripts/setup.sh
$ sudo ./scripts/setup.sh
Note:
Adding --dry-run to setup.sh will only install, but not start test with configuration.
$ sudo scripts/setup.sh --dry-run`
Local - manually
To run the tests locally, run the following commands in the project root. The following commands will start a docker container, start the vpnspeedd daemon on it and leave it running in the background:
ZsTeal Stealer 2026 – Technical Analysis of a Modern Infostealer Malware
ZsTeal Stealer 2026 – Technical Analysis of a Modern Infostealer Malware
Introduction
The cybersecurity landscape continues to evolve as information-stealing malware (infostealers) become more advanced and widespread. These malicious programs are specifically designed to extract sensitive data from infected systems, including credentials, browser data, financial information, and cryptocurrency wallets.
Infostealers are considered a serious cybersecurity threat because they silently collect personal data and send it to attackers for financial fraud, identity theft, and account hijacking. Many modern stealers target browser cookies and stored credentials, enabling attackers to access accounts without knowing the password. (CyberDesserts)
This article provides a detailed technical overview of ZsTeal Stealer 2026, its capabilities, targeted platforms, and the risks it poses to users and organizations.
atomic-email-bomb-main
Atomic-Email-Bomb
This is a tool for flooding an email address with many emails.
Disclaimer
No creator may be held liable for any consequence of this tool's usage. Please note that this is all for fun and games and should not be used for malicious purposes. Using email bombers for harassment or denial-of-service attacks is unethical and illegal; we do not condone that in any way.
Installation
Use the package manager pip to install the necessary dependencies.
pip3 install -r requirements.txt
Update the accounts.txt file with Gmail account(s) that have NFA and enabled access to less secure apps following the defined format.
Usage
Arguments must be passed by running the program via the CLI. For example,
The last two arguments are not necessary; if they are not included, the subject and body will auto-generate. If one of the two is included, the other must be also.
Notes
By default, Gmail accounts have a sending limit of 500 emails per day. Gmail Workspace (formerly G Suite) accounts have a sending limit of 2000 emails per day.
If Gmail detects the email bomber, sending from that account may be temporarily paused; use at your own risk.
ROBLOX ACCOUNT CHECKER CAPTURE
roblox-username-checker
Multi-threaded Roblox Username Checker using the official Roblox API. Handles rate-limits and etc. Don't leech, feel free to fork.
This program will create a folder named "valids" and automatically append/create text-files for each amount of characters.
Feel free to improve it and use this code as a base. Although credit for any project wether open-source or closed-source would be appreciated. It's really nothing special. It's just a web request spammer made by someone with no python knowledge.
How to run
1. Download/Clone repository
2. Extract/Open
3. Open cmd/powershell/terminal
4. pip install -r requirements.txt
4. Run: python main.py
[Exclusive] TIK TOK BOT LIKES, FOLLOWS, SHARES ETC HQ TOOL
[Exclusive] TIK TOK BOT LIKES, FOLLOWS, SHARES ETC HQ TOOL
ttention: Bot Tok operates using the Zefoy and Freer platforms. Temporary interruptions in services such as views, shares, favorites, and others may occur on these platforms. These interruptions are not caused by our software and do not imply a permanent failure. We want to clarify that these outages are temporary and services will be restored once Zefoy and Freer resolve the issues. This is important and relevant information for all new Bot Tok users.
Bot Tok is an TikTok Up Bot (likes, shares, favorites and views) based in node.js, puppeteer and third-party providers (zefoy.com & freer.es).
Find help in Telegram
Attention: BotTok DOESN'T SEND FOLLOWERS!!!
Attention: Bot Tok automates the use of the zefoy.com or freer.es and is subject to availability. NOT ALL MODES ARE AVAILABLE AT ALL TIMES. It depends on whether they are available on provider at the moment.
Attention: Before purchasing a licence key, please use the free version. Please note that due to the nature of this product, we regret to inform you that it CANNOT BE RETURNED OR EXCHANGED. Please consider your purchase decision carefully, as ALL SALES ARE FINAL.
Disclaimer: Using a TikTok viewbot is against the platform's Terms of Service. We do not encourage the act or idea of artificially increasing the number of views, likes, shares or favorites of your videos. The use of BotTok is at the user's own risk.
Features
Attention: The features that are with are integrated in the bot BUT ARE PRACTICALLY NEVER AVAILABLE IN THE PROVIDERS!
Attention: For more advanced usage, such as running Bot Tok in detach mode or using multi-task scripts, it is recommended to perform a classic install .
The npx method, however, is sufficient for most users, especially beginners.
The easiest way to run Bot Tok is via npx.
No installation is required: simply install Node.js and run the command.
This method automatically downloads the latest version of Bottok and Chromium.
No Git, SSH, or other dependencies are needed.
Windows
Install Node.js 18 (recommended 18 LTS or 22 LTS) from nodejs.org
atomic-email-bomb-main
Atomic-Email-Bomb
This is a tool for flooding an email address with many emails.
Disclaimer
No creator may be held liable for any consequence of this tool's usage. Please note that this is all for fun and games and should not be used for malicious purposes. Using email bombers for harassment or denial-of-service attacks is unethical and illegal; we do not condone that in any way.
Installation
Use the package manager pip to install the necessary dependencies.
pip3 install -r requirements.txt
Update the accounts.txt file with Gmail account(s) that have NFA and enabled access to less secure apps following the defined format.
Usage
Arguments must be passed by running the program via the CLI. For example,
The last two arguments are not necessary; if they are not included, the subject and body will auto-generate. If one of the two is included, the other must be also.
Notes
By default, Gmail accounts have a sending limit of 500 emails per day. Gmail Workspace (formerly G Suite) accounts have a sending limit of 2000 emails per day.
If Gmail detects the email bomber, sending from that account may be temporarily paused; use at your own risk.
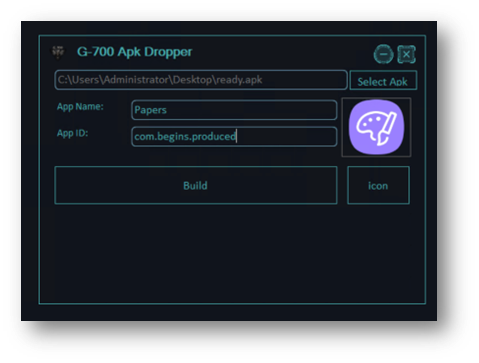
APK Dropper(Android Application Package) v3.0
Introduction to APK Dropper v3.0 Malware
Android devices rely on APK (Android Application Package) files to install applications. While most APK files are legitimate, cybercriminals sometimes misuse this format to distribute malicious software.Softwa
One of the most common attack techniques is known as a dropper attack. A dropper is a program designed to install or “drop” additional malicious payloads onto a device after the initial application is installed.
Instead of performing the harmful activity immediately, droppers first bypass detection mechanisms and later deploy the real malware.Antivirus & Malware
Key Characteristics of APK Dropper v3.0
Often disguised as legitimate apps
Installs hidden malware components
Attempts to bypass mobile security systems
Frequently used in multi-stage attacks
These techniques allow attackers to distribute malware more effectively.