JSpy is a remote monitoring and surveillance tool commonly associated with spyware-style activity,
designed to capture user actions, monitor device behavior, and collect sensitive information from
compromised systems. It is often promoted for stealth operation and persistent background
monitoring.
ATM card cloning refers to a category of fraudulent techniques and tools used to illegally copy magnetic stripe data from bank cards to create unauthorized duplicates. These activities are associated with ATM skimming, data theft, and financial fraud targeting banking systems. Modern banking security systems like EMV chips have significantly reduced the effectiveness of traditional cloning methods, but it remains a studied topic in cybersecurity research.
Key aspect
Magnetic stripe data capture and replication (conceptual attack vector)
Use of skimming techniques to extract card information
PIN capture methods (e.g., overlays or hidden cameras in attack scenarios)
Creation of counterfeit card duplicates for fraudulent use
Targeting of ATM and POS systems with weaker security
Bypassing legacy magnetic-stripe fallback systems (in older machines)
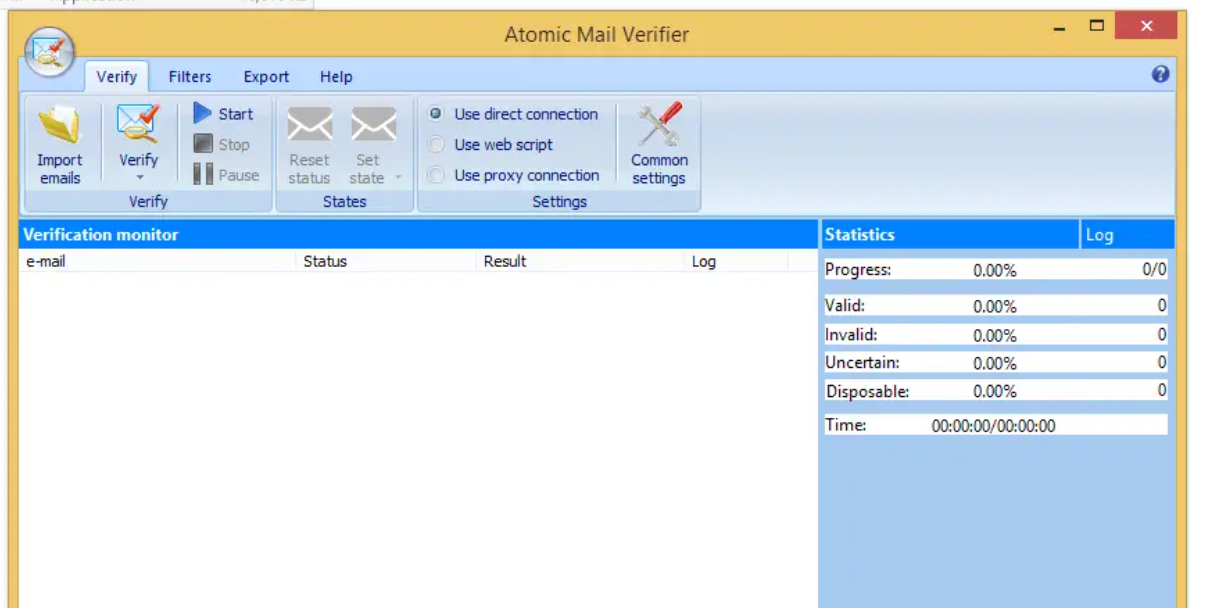
Atomic Email Verifier is an email list validation tool designed to check whether email addresses in a mailing list are real, active, and deliverable. It helps improve email marketing performance by removing invalid or fake email addresses and reducing bounce rates.
Key aspect
Three-step email validation (syntax, domain, and SMTP check)
Syntax checking to remove incorrectly formatted emails
Domain verification to confirm if the email domain exists
SMTP-level checking to verify mailbox existence
Bulk email list import from files (TXT, Excel, CSV, etc.)
Multi-threaded processing for faster verification
Proxy support (SOCKS4 / SOCKS5) for network handling
KJW0rm v0.5x is a cutting-edge cybersecurity tool designed to identify and neutralize digital threats in real-time. Its primary purpose is to enhance network security through automated vulnerability assessments, making it indispensable for IT professionals and organizations.
Features Overview
Real-Time Scanning: KJW0rm v0.5x offers continuous monitoring of networks and systems, instantly flagging suspicious activities to prevent breaches before they escalate.
Multi-Platform Compatibility: It supports seamless integration across Windows, Linux, and macOS, ensuring comprehensive coverage for diverse environments.
AI-Powered Threat Analysis: Leveraging machine learning algorithms, this feature analyzes patterns to predict potential attacks, providing proactive defense strategies.
Customizable Reporting: Users can generate detailed, exportable reports tailored to specific compliance needs, facilitating audit readiness.
Zero-Day Vulnerability Detection: It identifies unknown exploits through heuristic analysis, offering protection against emerging threats.
Warzone 2.70 is known in cybersecurity reports as a malicious Remote Access Tool (RAT) often distributed in cracked or pirated form. It is designed to secretly gain control over infected systems, steal data, and perform unauthorized remote operations. Security researchers classify it as a high-risk malware due to its strong data-stealing and injection capabilities.
Key aspect
Remote system control via C2 (Command & Control) servers
Credential and browser data theft
Process injection and payload execution
Persistence mechanisms (startup execution)
Anti-analysis and sandbox evasion techniques
Network communication for data exfiltration
Ability to drop and execute additional malicious files
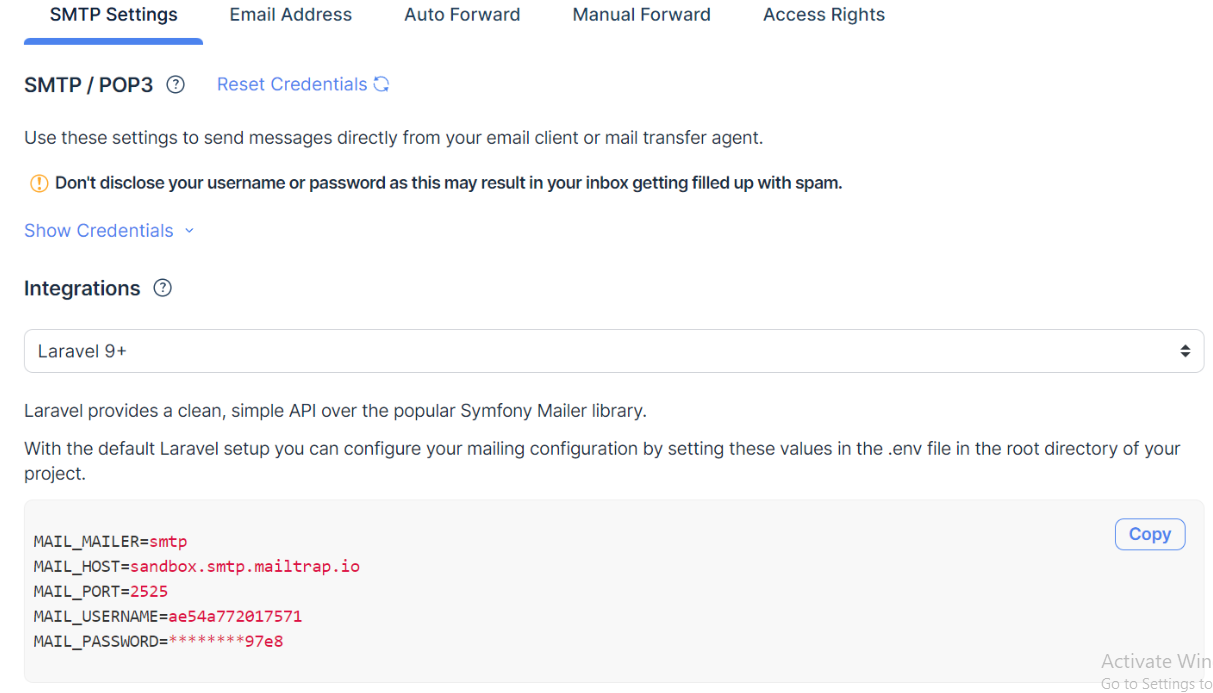
Laravel SMTP Checker 2025 is a powerful tool for testing and validating SMTP configurations in Laravel projects. It helps developers verify mail server connectivity, authentication, SSL/TLS support, port access, and email deliverability with fast diagnostics and real-time testing. Perfect for debugging Laravel mail issues, monitoring SMTP performance, and improving inbox delivery.
JackPos.v1.0 2026 is the ultra-fast 2026 cracked edition of the powerful Point-of-Sale data stealer. This fully unlocked version provides every premium feature without restrictions and delivers exceptional speed and stealth. It is built for users who need lightning-fast credit card harvesting, low resource usage, and reliable long-term operation on Windows POS systems.
Features Overview
Point of Sale (POS) management system
Fast billing & checkout support
Inventory stock management
Product barcode scanning
Customer management dashboard
Sales & purchase tracking
Invoice & receipt generation
Multi-user access system
Gorynych Diamond Fox HTTP Botnet 4.2.0 v650 with Tutorial
Short Intro
Gorynych Diamond Fox HTTP Botnet 4.2.0 v650 is a modular malware and HTTP-based botnet framework that became known in underground cybercrime communities for credential theft, keylogging, and remote control operations. It was designed to communicate with command-and-control (C2) servers through HTTP POST requests and supported plugin-based extensions for additional malicious activities.
Key aspect
HTTP-based Command & Control (C2) communication
Credential stealing and password recovery modules
Keylogger and browser data collection support
Plugin system for screenshots, mail theft, and payload delivery
Remote bot management dashboard
Encrypted data transmission using XOR encoding
NjRAT ACS Version 2024 represents the latest iteration of a notorious remote access trojan that has become a staple in cybercriminal operations. This enhanced version continues the legacy of its predecessors while incorporating advanced evasion techniques and expanded functionality,
Features Overview
eylogger (keystrokes capture)
File manager (upload/download/delete files)
Process manager (apps control/kill/run)
Registry/system modification access
Webcam & microphone spying (some builds)
Password stealing (browser data/cookies)
System info collection (IP, OS, hardware)
Command & Control (C2) remote server connection
Remote command execution (attacker control)
“HACK PACK Crypters, Binders, Keyloggers and more” refers to a category of tool collections discussed in cybersecurity threat analysis. These types of packages are often associated with malware development techniques and are studied by security researchers to understand how malicious software is created, hidden, and used in cyberattacks.
Key aspects
Includes concepts like file obfuscation and payload hiding (crypters)
Covers file combination techniques used in malware analysis (binders)
References input-monitoring behavior studied in keylogger research
Used in cybersecurity labs to understand malware construction methods
Helps researchers develop detection and prevention techniques
Supports training in identifying and mitigating cyber threats